3.27. Roles
PostgreSQL implements part of its access control using roles. These entities can own a set of privileges over the database objects and can be configured as a single user or a group of users. One particularity for roles is that, unlike the majority of objects, they are created at the database cluster level. In other words, a role is not associated with a specific database but with the server as a whole.
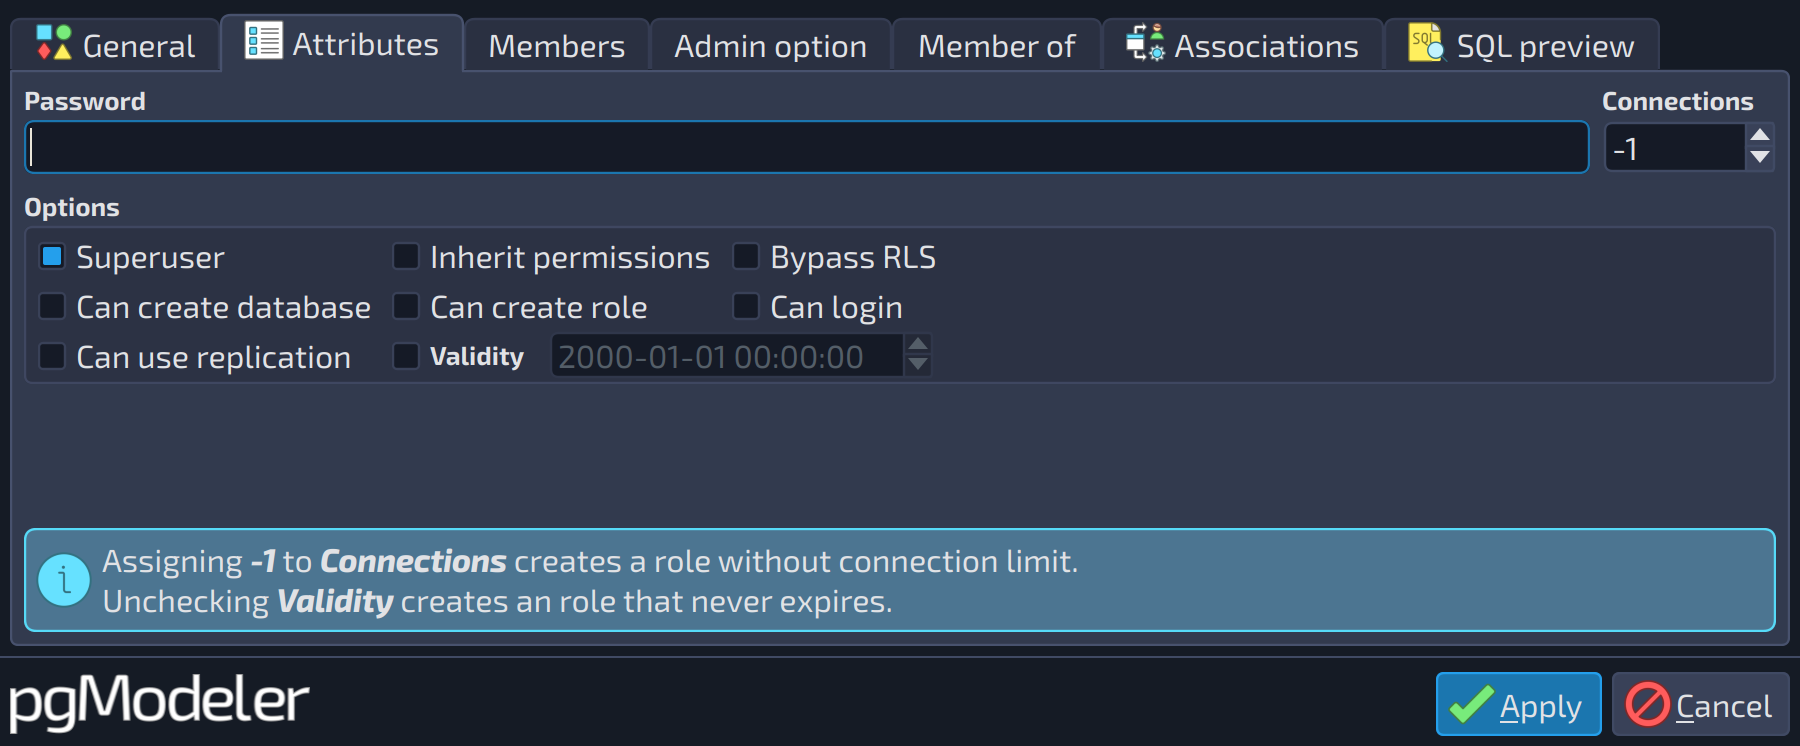 12345678910
| Attributes | |||
|---|---|---|---|
| # | Field | Group box | Description |
| 1 | Password | Defines a password for the role. It is used in password authentication, so it is meaningful for roles that can log in ( | |
| 2 | Connections | Specifies the number of concurrent connections the role can open. This attribute is used only if the role can log in to the server. The value | |
| 3 | Superuser | Options | Indicates that the role has full control over the server ( |
| 4 | Inherit permissions | Options | Indicates that the role will inherit the privileges of the roles listed in the |
| 5 | Bypass RLS | Options | Indicates that the role bypasses any row-level security on tables ( |
| 6 | Can create database | Options | Indicates that the role has permission to create databases ( |
| 7 | Can create role | Options | Indicates that the role can create other roles on the server ( |
| 8 | Can login | Options | Indicates that the role can log in to the server ( |
| 9 | Can use replication | Options | Indicates that the role can control the replication feature on the server ( |
| 10 | Validity | Options | Specifies the date and time after which the role's password is no longer valid ( |
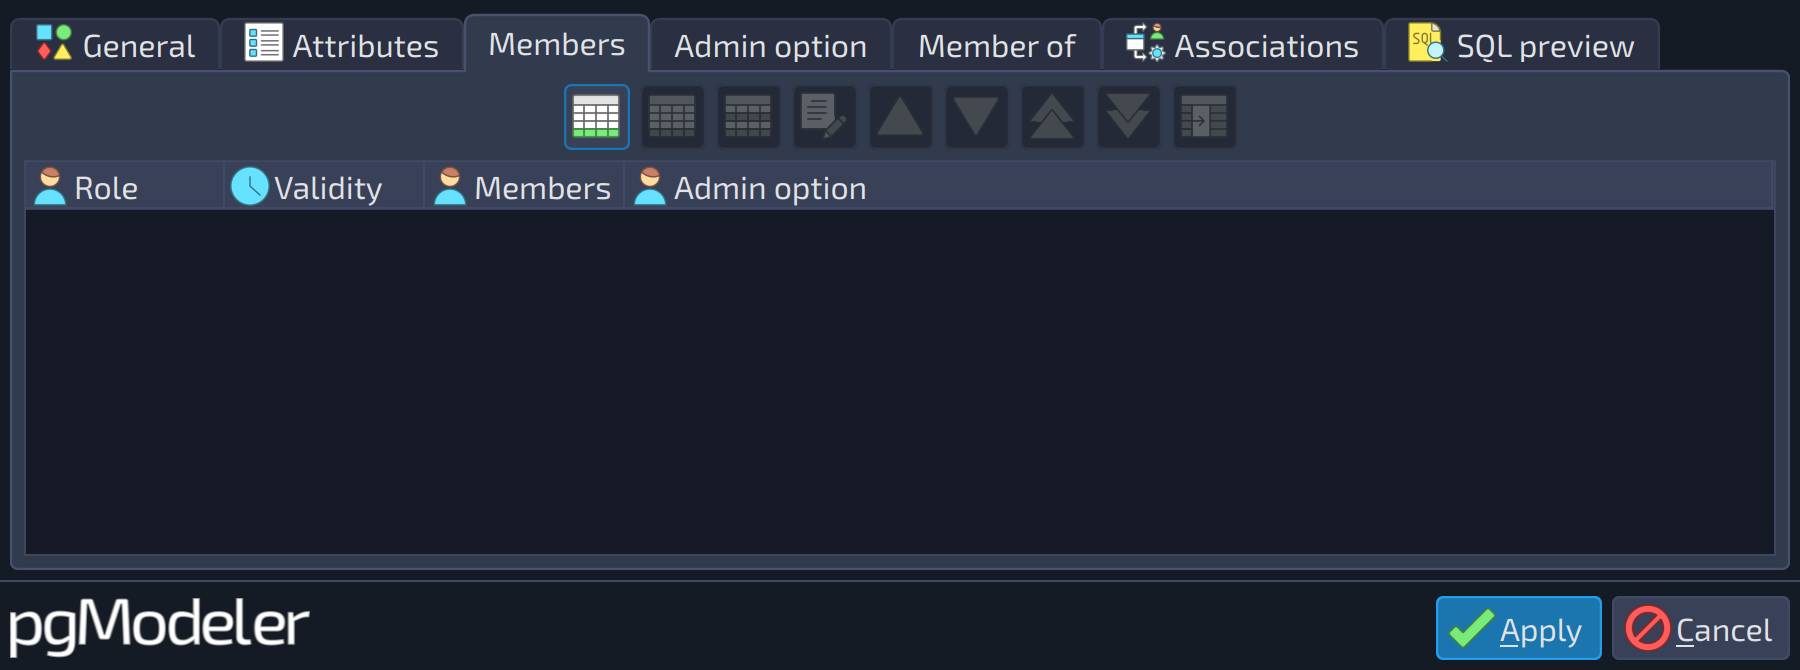 1
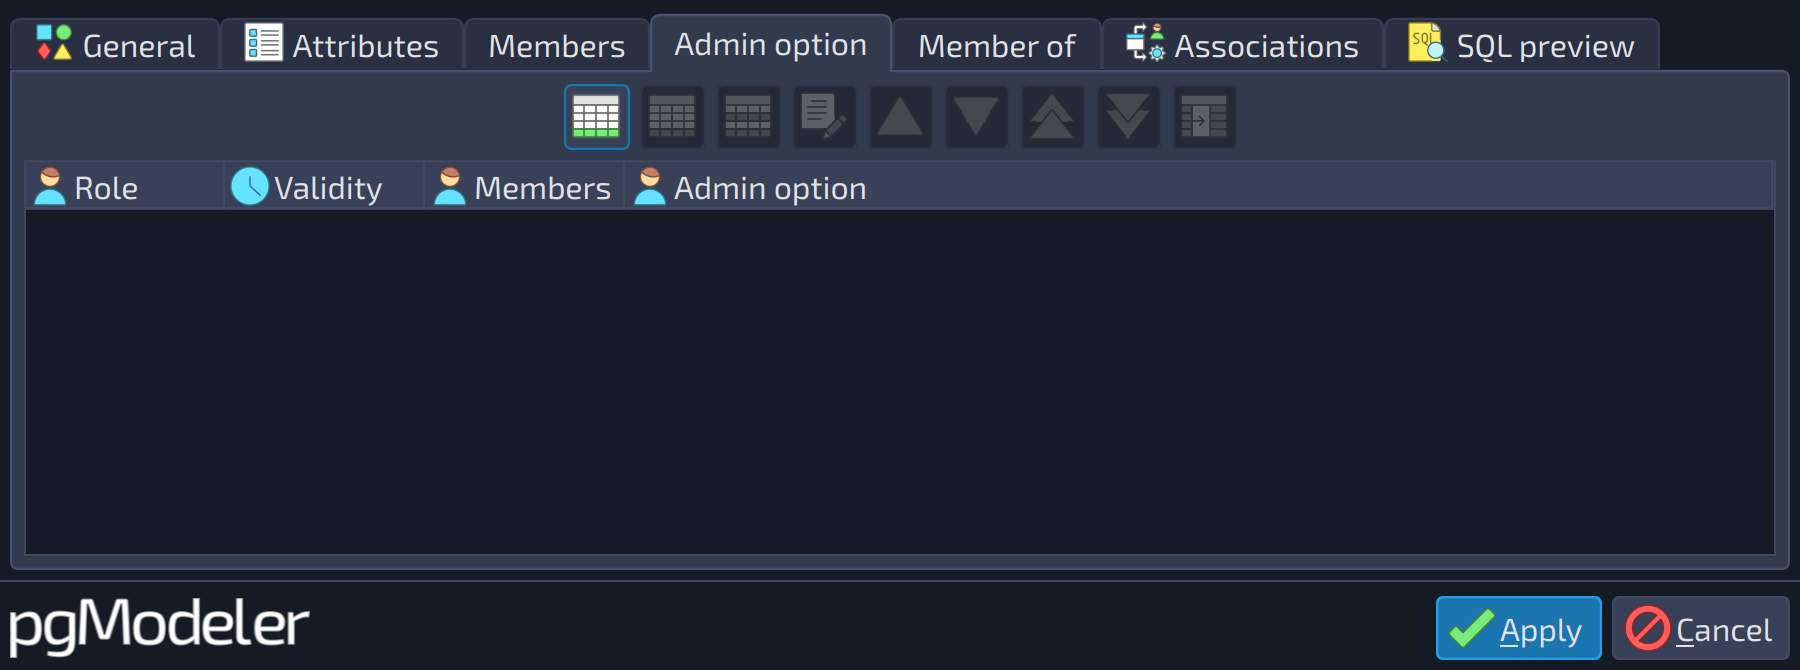
| Members | ||
|---|---|---|
| # | Field | Description |
| 1 | Members | The roles that are added as members of the role being handled ( |
 or remove
 them.
 1
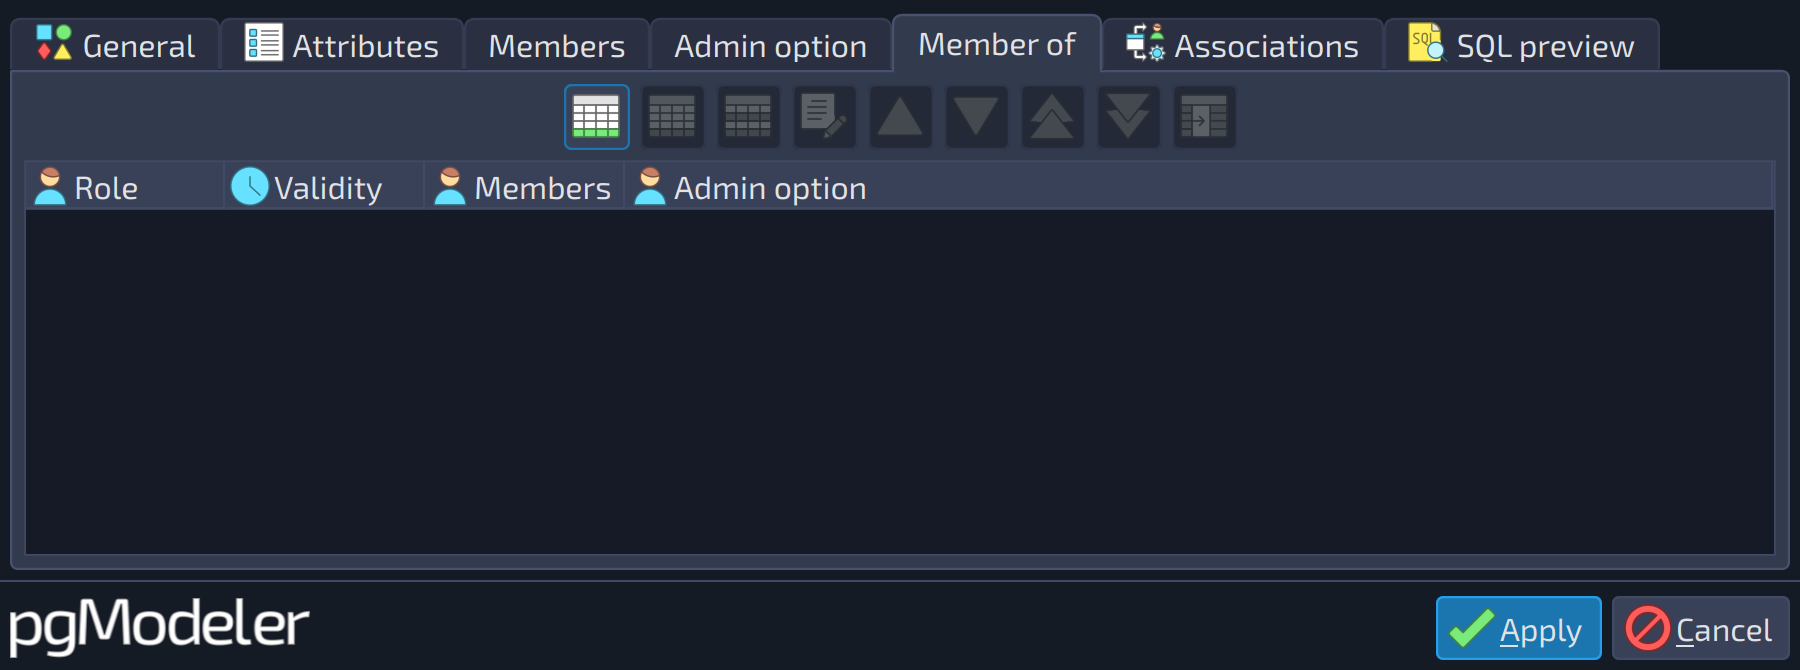
| Admin option | ||
|---|---|---|
| # | Field | Description |
| 1 | Admin option | The roles that are added as members of the role being handled with |
 1
| Member of | ||
|---|---|---|
| # | Field | Description |
| 1 | Member of | The roles of which the role being handled is a member ( |
References
Role DDL
https://www.postgresql.org/docs/current/static/sql-createrole.html